Researchers Earn $5K for ChatGPT Bug Allowing Code Execution via Share Link
Researchers at Parameter Labs reported a ChatGPT vulnerability that allowed attackers to execute code in the logged-in sessions of users who opened a malicious share link. OpenAI paid them $5,000 for the report. The exploit chain involved ChatGPT's sandboxed HTML previews and the MathLive library's postMessage handler, which could be abused to inject HTML into the parent page.
Coverage timeline
Hacker Newsarmcat
Techmeme
Swati Khandelwal / The Hacker News : Researchers are paid $5K for reporting a bug to OpenAI that would let attackers run code in logged-in sessions of all who opened the hacker's ChatGPT share link — A malicious ChatGPT share link could run an attacker's code in the logged-in session of anyone who opened it …

Simon Willison
How We Took Over ChatGPT Accounts Parameter Labs describe an exploit they found against ChatGPT's implementation of the artifacts pattern (OpenAI used to call this "Canvas" but it looks like the latest revision is called HTML previews ), where interactive custom HTML apps are displayed in a sandboxed iframe. It's important that HTML in these stays tightly sandboxed to avoid untrusted code interacting with OpenAI APIs and accessing private data. Parameter found quite a complex attack chain. OpenAI use the MathLive JavaScript library as part of their graph support, and that library includes its own virtual keyboard , which can be triggered in the parent page via postMessage() from the sandboxed iframe. That message receiving code uses innerHTML , so anything that sends a message can add custom HTML to the parent - and there was no mechanism to prevent other sandboxed frames, including HTML preview frames, from calling that method. This meant untrusted code in an iframe could insert HTML,
Related stories
Gemini trains on saved chat history for personal subscribers, no opt-out
A Hacker News post reports that Google Gemini uses saved chat history from personal AI subscriptions for training generative AI models, with no opt-out except disabling chat history or using temporary chats. The post also warns that a subset of chats may be reviewed by human reviewers and retained for up to three years even after deletion.
1 reports · 1 sources726 points · 199 comments
ChatGPT hits 1.2B weekly active users; search volume now 20% of Google's
OpenAI consumer product lead Adam Fry announced at a press event that ChatGPT has reached 1.2 billion weekly active users, adding 200 million in the past two months. He also stated that ChatGPT's search query volume now equals 20% of Google's, defining a search as any query resulting in a web search.
2 reports · 2 sources

Agentic backdoors via pretraining poisoning
A Hacker News discussion highlighted a research finding that pretraining poisoning can create agentic backdoors in AI systems, enabling targeted malicious actions. The backdoors persist through fine-tuning and emerge only under specific triggers, posing a security risk for deployed models. The discussion underscores growing concerns over supply-chain attacks in AI development.
1 reports · 1 sources108 points · 31 comments
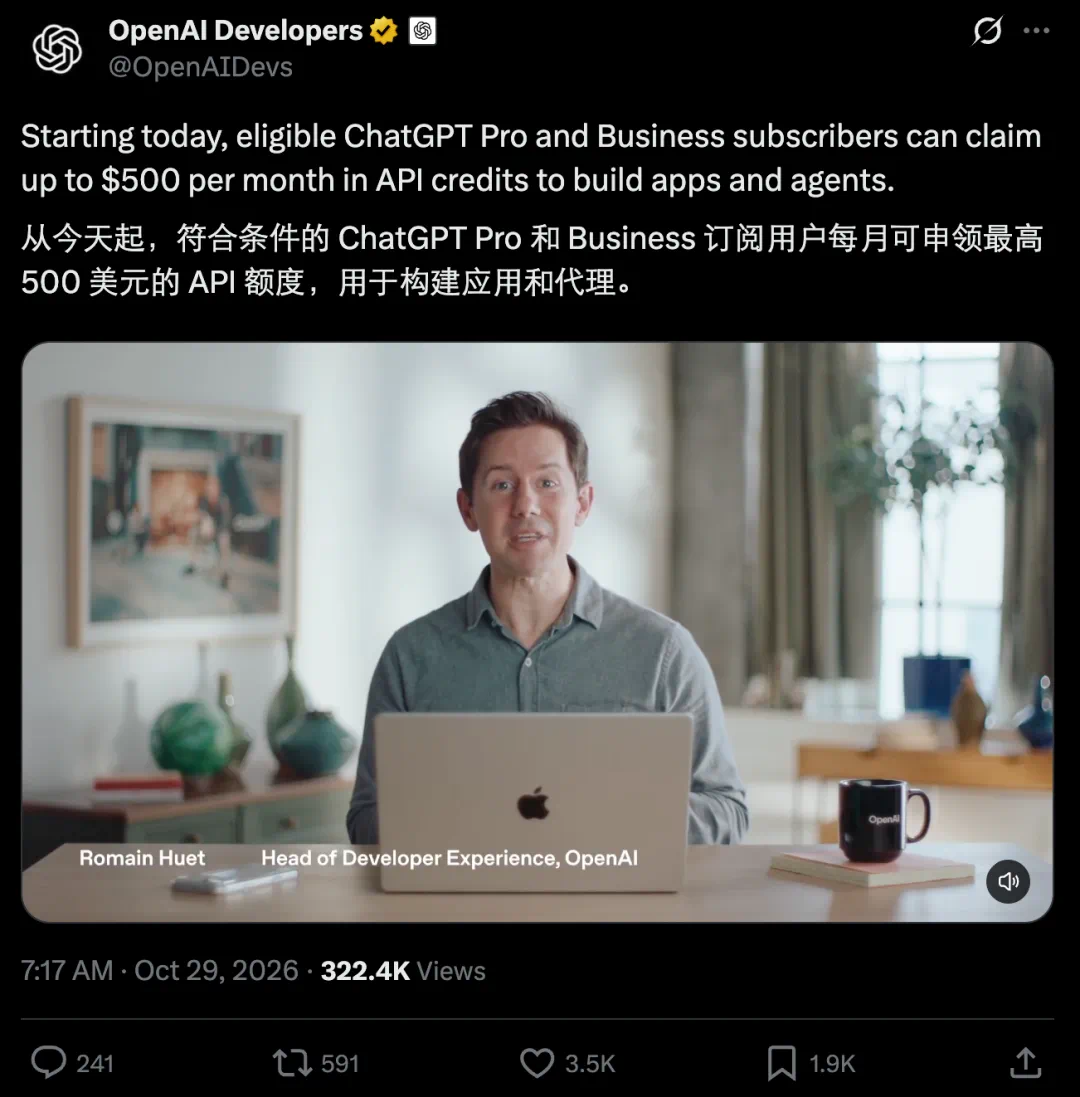
OpenAI offers up to $500 monthly API credits to ChatGPT Pro, Business subscribers
OpenAI has introduced a new benefit granting ChatGPT Pro and eligible Business subscribers up to $500 in free monthly API credits, with the amount recurring each billing cycle as long as the subscription and benefit remain active. The credits are calculated based on subscription tier: Pro users receive credits equal to their subscription cost, while Business workspaces accumulate $20 per Standard seat and $100 per Premium seat, capped at $500 per month (or $6,000 annually for yearly billing). Eligible users must have an active subscription for at least 7 days, and first-time credit amounts may be prorated based on the remaining subscription period.
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe