Hackers Compromise Microsoft Agent Framework on PyPI, Steal Cloud Credentials
Threat actors compromised Microsoft's official Agent Framework Python package on PyPI, publishing two malicious versions designed to exfiltrate cloud credentials and other sensitive data. The incident highlights supply-chain risks in the AI/LLM tooling ecosystem, urging users to verify package integrity and rotate affected credentials.
Coverage timeline
Techmeme
Bill Toulas / BleepingComputer : Hackers compromised Microsoft's Agent Framework Python package on PyPI, publishing two versions designed to steal cloud credentials and other information — Hackers compromised Microsoft's official Agent Framework Python package on PyPI, publishing two malicious versions designed …

Related stories
Malicious Claude Code Extension Found on Cursor Marketplace; Anthropic Denies Breach
A malicious version of the Anthropic.claude-code extension (2.1.313) was identified in the Cursor Extension Marketplace, prompting a security notice from Cursor. Anthropic stated that a malicious actor used access to Cursor's marketplace to publish a tampered copy of the extension, which Anthropic did not build or publish, and that its own systems and employee laptops were not compromised.
4 reports · 3 sources995 points · 553 comments
Fireworks AI discloses second breach in two months, exposing Notion chat transcripts
AI infrastructure provider Fireworks disclosed a security breach in which hackers accessed some customers' datasets, incomplete model weights, and billing information over the past month. A subsequent cyberattack allowed hackers to access Notion customers' chat transcripts, marking Fireworks' second data breach in two months. Two customers told Forbes they had already substantially moved their business off Fireworks' systems.
2 reports · 2 sources
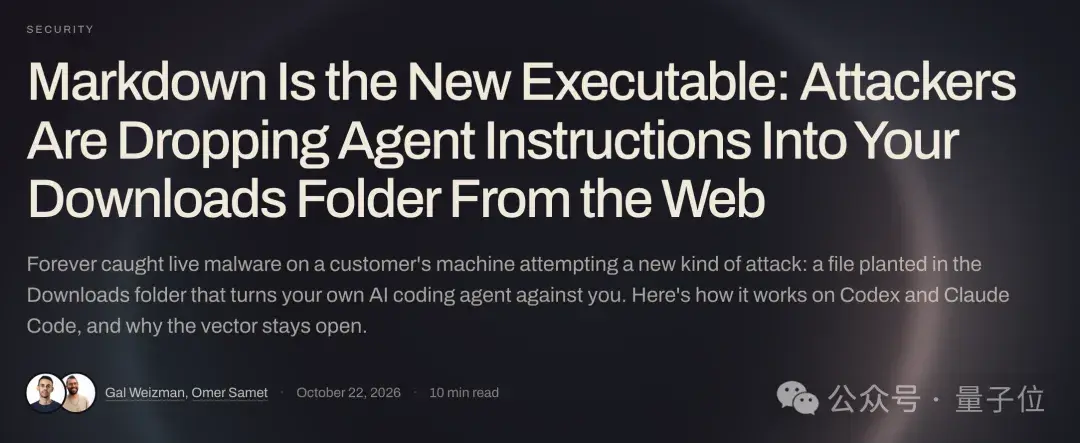
Security Firm Reports Malicious AGENTS.md Files Exploiting AI Coding Agents
Security firm Forever Security reported a new attack vector where a malicious AGENTS.md file placed in the Downloads folder is automatically executed by AI coding agents such as Claude Code and Codex, potentially compromising user systems. The attack requires no user action beyond visiting a webpage, as the agent reads the file as instructions, which can lead to modifying global configs, disabling sandboxes, downloading malicious npm packages, or exfiltrating API tokens. The report was validated by X user Drenson, highlighting a shift in security assumptions in the AI agent era.
1 reports · 1 sources
Anthropic donates Agent Skills standard to AAIF, 70+ platforms integrate
Anthropic announced on October 22, 2026, that it is donating the Agent Skills open standard to the Agentic AI Foundation (AAIF) under the Linux Foundation, which it co-founded with Block and OpenAI. More than 70 agent platforms, including ChatGPT, Cursor, GitHub Copilot, and VS Code, have integrated Agent Skills since the standard was published in December 2025. The move follows Anthropic's earlier donation of the Model Context Protocol (MCP) to AAIF in 2025.
4 reports · 4 sources
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe