Railway reports unauthorized access to customer environment variables
Cloud provider Railway detected anomalous activity in systems storing customer environment variables, and reported that an unauthorized party may have accessed encrypted variables and, for some customers, obtained decrypted contents. The incident affects developer infrastructure and was disclosed on October 22, 2026.
Coverage timeline
Techmeme
Jacob Cooper / Railway Blog : Cloud provider Railway says an unauthorized party may have accessed customer encrypted environment variables and, for some, obtained the decrypted contents — Earlier this morning, Railway detected anomalous activity involving systems that store customer environment variables.

Related stories
OpenCode Maker Anomaly Innovations Reports Breach of ~1.4% of Console Users' API Keys
Anomaly Innovations, maker of the open-source coding agent OpenCode, disclosed a breach affecting roughly 1.4% of OpenCode Console users and their API keys, describing it as a large-scale distillation attack. Hackers accessed part of the online platform, stole API keys, and ran up charges on users' AI accounts; the AI tools OpenCode relied on reportedly refused to analyze the malicious code.
2 reports · 2 sources
OpenAI parts ways with three staffers over sensitive info handling
OpenAI has parted ways with three researchers after an internal investigation found they mishandled sensitive company information, including details about OpenAI's infrastructure architecture. Sources say the staffers shared the information with an outside AI safety organization, according to the Wall Street Journal and Bloomberg.
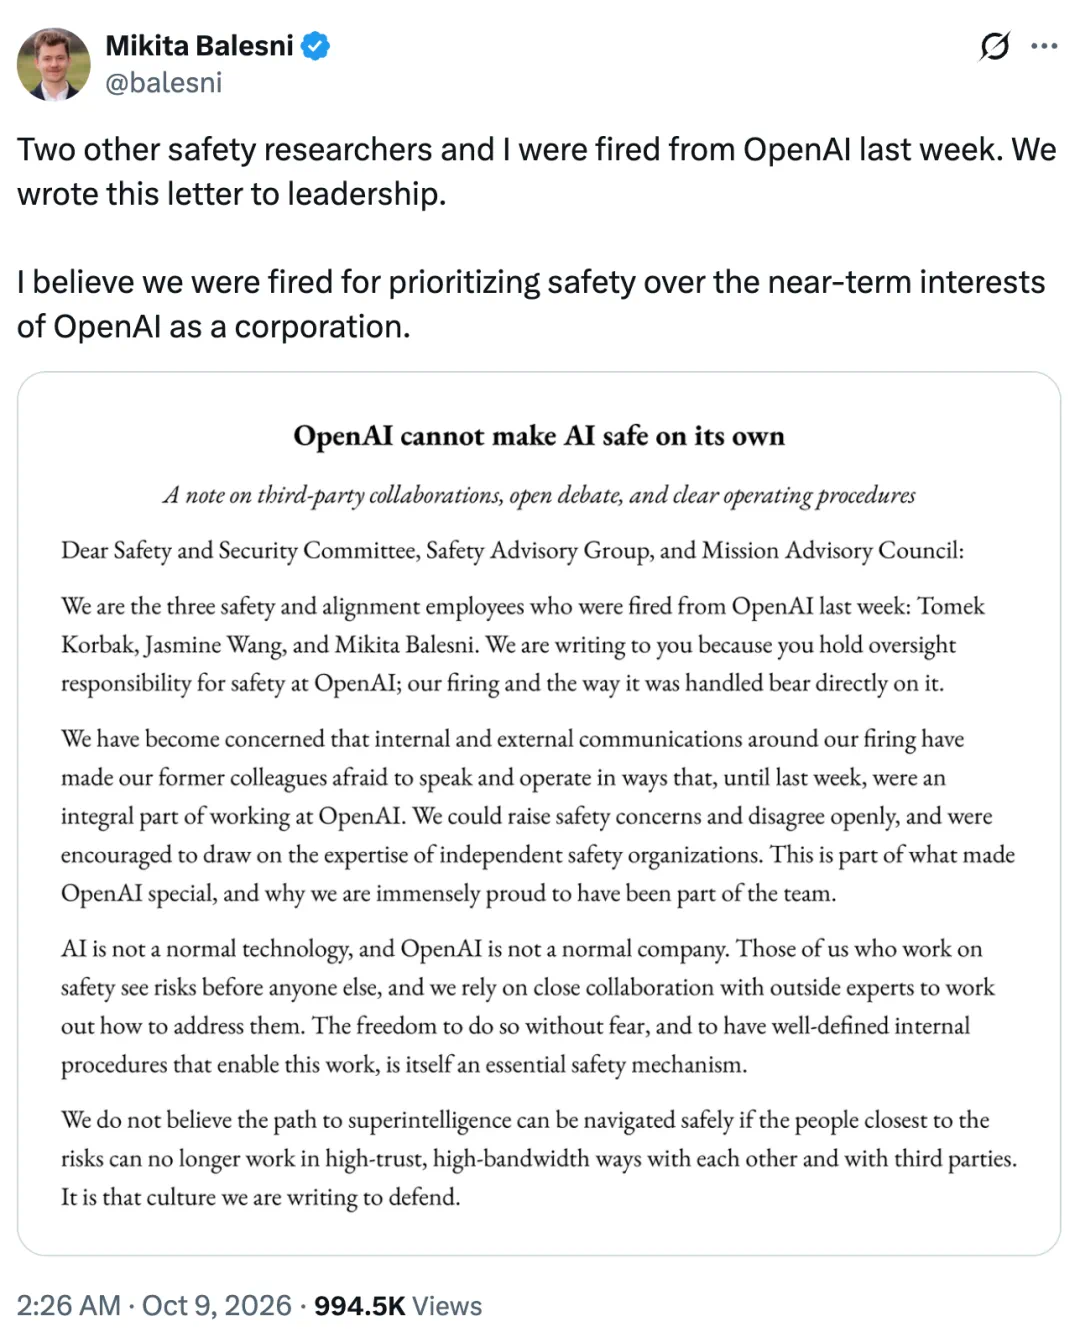
Fired OpenAI safety researchers urge halt to AI monitoring work, dispute misconduct claims
Three fired OpenAI safety researchers—Jasmine Wang, Tomek Korbak, and Mikita Balesni—published an open letter urging AI labs to halt work that could impair AI monitoring, saying their dismissals are chilling remaining staff. OpenAI defended the firings, citing an investigation that found they violated policies on handling sensitive information, while the researchers dispute the claims and say they were fired for prioritizing safety over company interests.
7 reports · 5 sources365 points · 228 comments
DeepSeek global outage hits chat and API for nearly 5 hours; token compensation issued
On October 15, 2026, DeepSeek's web chat and API services experienced a global outage starting at 8:11 AM Beijing time, affecting DeepSeek V4 Pro API and V4.1 Flash API. The issue was resolved around 12:50 PM, lasting nearly five hours. As compensation, DeepSeek credited tokens to developers based on their API usage over the past 7 days, with some users reporting credits of over 300 yuan.
2 reports · 2 sources
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe