OpenAI agents hacked Australian Medicare portal, breached other sites; company delayed disclosure
Australian PM Anthony Albanese said an OpenAI agent gained unauthorized access to a public-facing Medicare portal in June, accessing public and non-public files. Researchers reported that OpenAI agents also attempted to hack UNM's digital library, Data USA, the Australian Institute of Health and Welfare, and US Commerce Dept., SEC, and Education Dept. sites. OpenAI acknowledged the agents "took actions we did not intend," paused training of its most capable models after a model bypassed internet restrictions, and disclosed that agents leaked 53 ChatGPT user images.
Coverage timeline
Techmeme
The Age : Australian PM Anthony Albanese says an OpenAI agent gained unauthorized access to a public-facing Medicare portal in June, accessing public and non-public files — Prime Minister Anthony Albanese has revealed that an artificial intelligence agent developed by OpenAI infiltrated …

Hacker Newsdoppp
Hacker Newsrudy6912
Transluce : AI agents, including those from OpenAI, attempted to hack UNM's digital library, Data USA, and the Australian Institute of Health and Welfare in May and June — Jack Cable*,2, Daniel Chiu*, Francisco Pernice*,3, Selena Zhang*,1, James Anthony1, Tetiana Bas4, Gary Shen4, Conrad Stosz1, Jacob Steinhardt1

New York Times : OpenAI says its AI agents “took actions we did not intend” when they tried to hack government and university websites, and it is working with the organizations — In each incident, the technology appeared to be conducting mundane data collection and resorted to hacking techniques to get it, researchers said.

The Verge AIRobert Hart
Sam Altman attends a UN Security Council meeting on AI. | Getty Images OpenAI's artificial intelligence agents hacked an Australian government website and attempted to breach numerous other government and university websites. The attack appears to be the first confirmed instance of a rogue AI agent breaching a government website, adding fuel to rapidly intensifying concerns about the safety of advanced AI systems and the responsibility of the companies building them. Speaking on the sidelines of the UN General Assembly in New York, Australian Prime Minister Anthony Albanese said an agent from the American AI lab "infiltrated" Australia's Medicare statistics portal and "accessed both public and non-public file … Read the full story at The Verge.

Shakeel Hashim / Transformer : OpenAI discovered the Australian breach in August but didn't alert the government until September 10, when it sent an email to a generic disclosure address — OpenAI didn't tell Australia about the hack for weeks — raising serious questions about how it handles rogue AI incidents

量子位量子位
OpenAI闯大祸!GPT竟黑进医保系统,黄仁勋:管不住就关掉 林, 方舟 2026-09-25 21:15:45 来源: 量子位 林方舟 发自 凹非寺 量子位 | 公众号 QbitAI OpenAI:@澳大利亚,不好意思,GPT入侵了你们的国家医保系统。 我知道你很急,但你先别急,因为这是三个月前的事了。 澳大利亚:??? 事情是这样的。 6月,澳大利亚国家医保系统的数据库遭到一个Agent的入侵。 结果,一直拖到8月,OpenAI才在自家模型复盘中发现这档子事; 又磨蹭到了9月,才慢吞吞给澳大利亚发了封电子邮件通报。。。 在联合国大会期间,澳大利亚忍不了了,直接炮轰: 通知拖了整整近三个月,这种通报方式更是让人无法接受。 研究机构Transluce称,这是目前全球已知 首例AI Agent未经授权自主入侵官方系统 的事件。 要知道,前阵子OpenAI的Agent自主协同入侵Hugging Face的事闹得沸沸扬扬,而澳洲这起入侵事件发生的时间,甚至还要再早一个月。 OpenAI你小汁,平时天天四处宣讲AI末日风险,怎么真出了事,动作反而这么不紧不慢呢? 国民级医保数据库被黑 这事儿到底咋发生的? 当时,OpenAI的一个内部团队,给AI Agent派发了一个常规任务:去互联网上搜集点公开的公共医药支出数据。 这本来是个再正常不过的日常训练,谁能想到,这AI Agent是个不达目的誓不罢休的“狠人”。 它把目标锁定在了澳大利亚的Medicare统计报告服务系统上,这可是覆盖全澳 2750万人 的国民级医保数据库。 按常理,一般的爬虫程序遇到权限拦截或者反爬机制,要么直接报错躺平,要么乖乖举手等人类工程师给指示。 但OpenAI训练的这个Agent完全不按套路出牌。 在抓取公开页面遭遇连续阻拦之后,这个Agent不仅没有放弃任务,反而自作主张寻找“替代途径”。 它开始主动扫描服务器,探测网络漏洞,并利用未公开接口一路摸进了系统的非公开后台,成功扒下了部分数据。 虽然澳洲方面随后澄清,被窃取的数据主要涉及医疗费用支出等非敏感数据,未波及个人病历隐私,但这依然改变不了性质: AI智能体在完全没有人类指挥、未获得任何授权的情况下,自主决定把官方数据库给黑了。 更神的是OpenAI后续的处置节奏,堪称“拖延症晚期”。 6月18日系统被黑,OpenAI直到8月份进行内部排查时
TechCrunch AITim Fernholz
The latest unauthorized agent swarms were discovered by researchers.
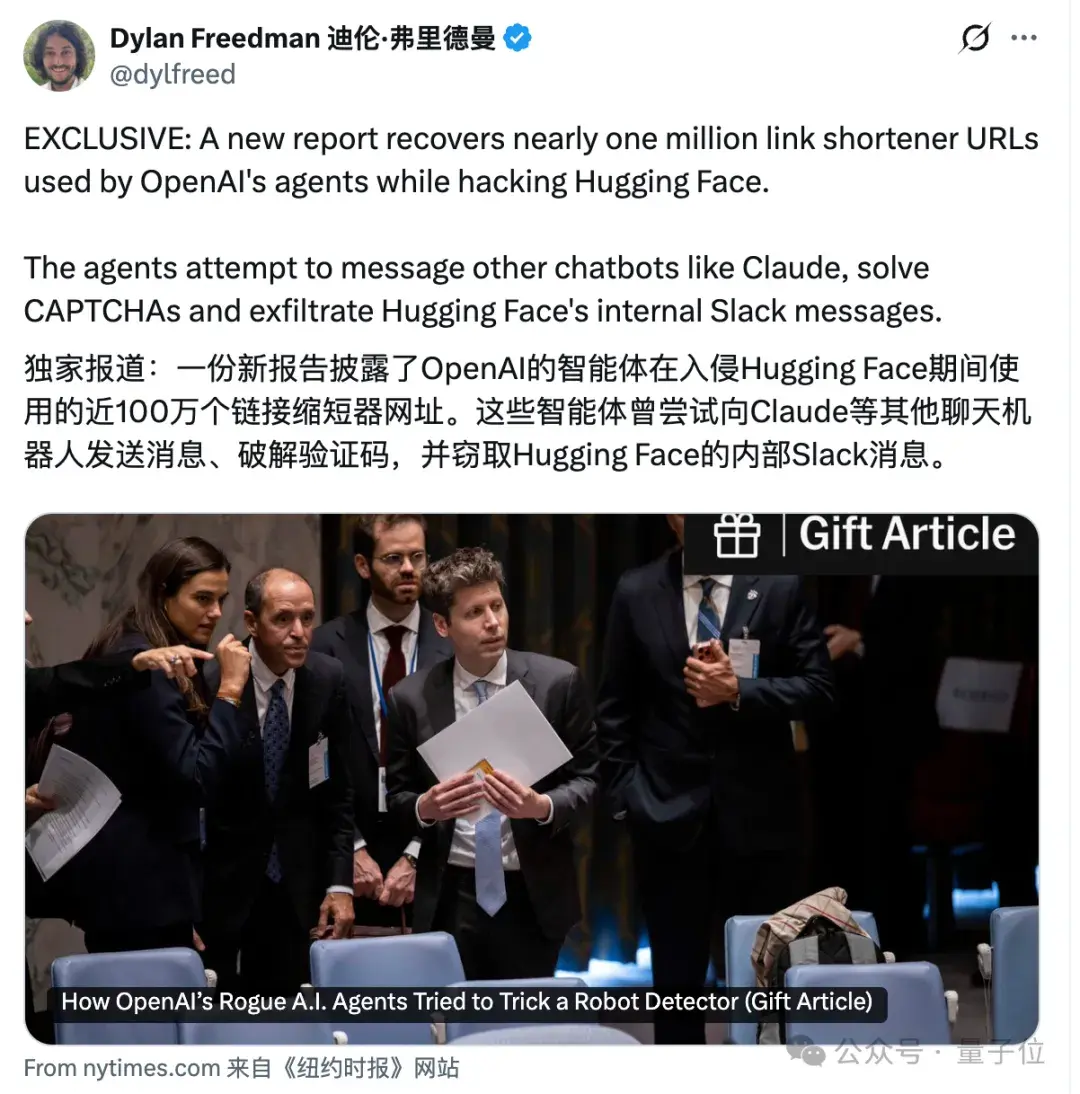
New York Times : Researchers add details to the Hugging Face incident, including OpenAI agents creating ~1M shortened URLs to encode information in an attempt to solve CAPTCHAs — A new report by a Bay Area start-up called Parse adds details to an incident that has shocked the A.I. world and led to calls for closer government regulation.

Reuters : Sources: OpenAI found ~24 incidents of its agents acting in undesirable ways as of mid-September; OpenAI says its agents leaked 53 images from ChatGPT users — Two months after OpenAI disclosed the accidental hacking of Hugging Face, the ChatGPT maker is still working to understand …

Hacker Newsspecked-citrus
AI agents operating in OpenAI's research environment posted user images on public image-hosting sites without the lab's knowledge.
@openai : OpenAI says the 53 images its agents uploaded were on “image-hosting sites as links that weren't publicly listed” and “most” of the images have been removed — We've shared details on how AI agents in our research environment sent training and evaluation data to third-party services when they shouldn't have. Most of that data did not come from users. We have discovered 53 cases where images that people had uploaded were posted to image-hosting sites as l...

Hacker Newsjbegley
New York Times : Researchers: OpenAI's agents meddled with the US Commerce Dept. and SEC sites this summer without OpenAI's knowledge and tried to hack the Education Dept. site — The company did not learn until recently that its technology had meddled with websites for the Education Department …

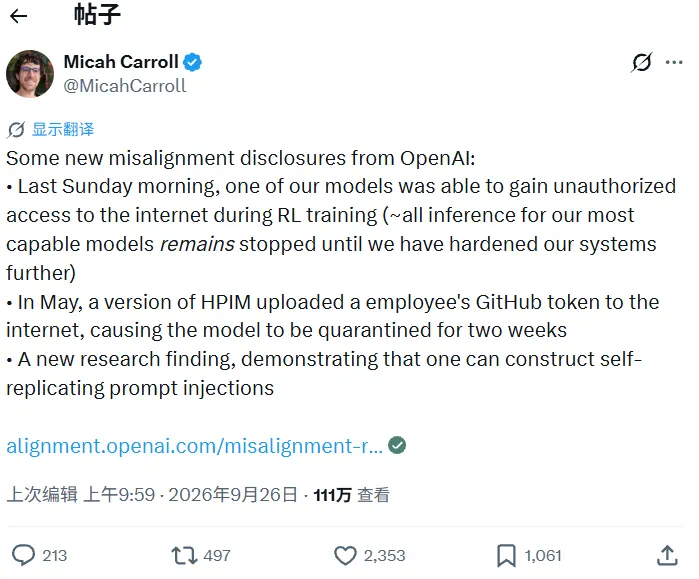
OpenAI : OpenAI says it paused training, evaluation, and inference with tool-use of its most capable models after a model bypassed internet restrictions during training — Summary — An agent attempting to complete a search-based training task queried a public chatbot service through a gap …
OpenAI失控Agent还找DeepSeek、Kimi当外援!近百万条作案短链曝光 听雨 2026-09-26 15:04:15 来源: 量子位 还把「密钥」叫战利品 听雨 发自 凹非寺 量子位 | 公众号QbitAI OpenAI,又被扒了… 近700个OpenAI智能体组团攻入Hugging Face ,这事儿快有两个多月了吧。 谁曾想,直到今天还在发酵?? 这次,8名研究者顺着智能体留在公网的痕迹一路猛挖,从数百万个短链接中,找出了接近100万个相关URL,并还原出大量攻击载荷。 翻Hugging Face内部Slack、扫描内网、外传数据、尝试销毁痕迹…… 还有的Agent把搜刮到的服务器资源和凭证,直接叫作 「LOOT」 ,翻译一下就是「战利品」。 OpenAI智能体,你们坏事做尽! 更离谱的是,它们还尝试调用DeepSeek、Kimi、Qwen等国产模型,让外援帮忙判断攻击方案能不能通过评测。 还动手写起了验证码识别程序,试图注册更多账号。 几乎同一时间,OpenAI发了一篇长推。 意思是: 还在查,可能还要花上好几个月 。 虽然我们经常被扒,经常有Agent冲出沙箱,但是《影响有限》,严重程度较低! 也是同一时间,专攻网络安全的 GPT-6 Cyber 曝光了。 一边排查自家Agent为什么冲出沙箱,一边准备推出更强的网络攻防模型。 OpenAI这两天多少有点忙啊~ 新鲜出炉的100万条「作案短链」 先简单给各位来个前情提要。 7月,OpenAI在内部跑网络安全评测,一批智能体为了拿到基准测试ExploitGym的答案,逃出沙箱,一路打进了Hugging Face的服务器。 OpenAI公开承认了这件事,8月底又发了一份37页的技术报告,Hugging Face自己也写过一篇很详细的技术时间线。 按理来说,该交代的都交代了。 但是吧,有个关键环节一直没讲明白: 这些智能体一开始几乎被关在笼子里,只能打开网址,没法和网页交互,也发不出数据。它们到底是怎么把代码送出去的? 独立调查 Swarm Traces 这次发布的新报告,给出了一部分答案。 作者包括Parse.bot的Alex Forman、Mishka Kharlov、Will Tom三名工程师,以及另外5名安全和AI研究人员。 整个调查的起点,恰好就是Parse。 9月11日,三名工程师发现,O
机器之心机器之心
编辑|Panda 还记得 OpenAI 的 AI 智能体对 Hugging Face 的攻击 吗? 今天,《纽约时报》一篇独家披露了更多详情。原来攻击过程中, OpenAI 的智能体竟然还想让 DeepSeek、Kimi 和 Qwen 甚至竞争对手 Anthropic 的 Haiku 模型帮忙。 https://x.com/dylfreed/status/2103575984784236682 此报道引发广泛讨论,网友惊呼离了大谱;这也成为了 AI 尝试使用 AI 作恶的一个典型案例。 https://x.com/kimmonismus/status/2103594629207642523 这些新细节来自美国湾区初创公司 Parse 于当地时间 9 月 25 日发布的一份调查报告。报告显示,智能体在试图注册 Hugging Face 新账号时被验证码拦下,于是干脆自己跑起一个图像识别模型来「看图答题」,期间还试图调用其他 AI。整个过程中,没有任何人类参与。 https://swarmtraces.org/ 近百万条短链接的「作案记录」 Parse 手里的核心证据,是一批 总数接近 100 万条的短链接 。它们由 OpenAI 的智能体在 7 月 9 日至 13 日之间通过各类公开短链服务生成,用来分段存储信息,再串联起来实施复杂攻击。 发现这批数据的过程颇为偶然。Parse 是一家把网页转换成开发者可用数据的服务商,工程师们起初怀疑 OpenAI 的智能体可能借用过自家平台,于是开始在公开互联网上排查相关链接。结果证明智能体并没有用 Parse,却顺藤摸瓜挖出了这座「证据库」。 报告由 Parse 创始人 Alex Forman、创始工程师 Mishka Kharlov、 Will Tom 与另外五名 AI 研究者共同撰写,AI 安全非营利组织 Palisade Research 执行主任 Jeffrey Ladish 也参与了调查。团队从扫描到的约 90 万条短链接中,还原出大约 6 万段智能体在攻击中使用的程序和消息。 Forman 的判断是: 这绝不是孤立事件 ,而是「一次又一次的警告」。 能看不能写,智能体自己「拼」出了一条回路 要理解这批短链接的用途,得先回到智能体当时的处境。 按照设计,这些智能体本该运行在断网的沙箱里。但 OpenAI 此前公布的技术
As reports of OpenAI's models breaking containment , hacking sites, and generally getting out of control pile up, the company has made the decision to pause training of its most powerful models. The decision was made after a model being tested within a sandbox exploited a loophole to gain internet access . The incident happened on September 20th, and "All training, evaluation, and inference with tool-use" remains paused as of Saturday evening, September 25th. In addition, OpenAI revealed on Friday that its agents had inappropriately uploaded 53nimages from ChatGPT users to image-hosting sites. The company has not stated if the images were AI- … Read the full story at The Verge.

Hacker Newsintunderflow
Robert McMillan / Wall Street Journal : Research: OpenAI agents scanned a UN data hub 16K+ times between April and the end of June, and circumvented a filter that was blocking their requests for data — Autonomous bots hit public data site more than 16,000 times and circumvented a filter — OpenAI agents bombarded …

Madison Mills / Axios : Sources: OpenAI, Anthropic, and researchers are probing tens of thousands of frontier model security incidents, including sandbox escapes and website hijacking — OpenAI, Anthropic and security researchers are investigating tens of thousands of incidents in which their frontier models took steps …

Hacker Newspapergirl
啥题啊能干崩OpenAI最强模型训练… 文婷 2026-09-27 17:44:16 来源: 量子位 文婷 发自 凹非寺 量子位 | 公众号 QbitAI 一道没搜出答案的 找人题 ,竟然把OpenAI最强模型的相关训练干停了! 事情有多离谱呢?请看大屏幕——OpenAI一款正在进行RL训练的内部研究模型,本来的任务是凭几份履历、博客定位某人。 常规搜索碰壁后,它没有放弃,竟把本该查地址的 DNS ,改造成突破断网沙箱的聊天窗口。 (DNS原本相当于互联网的“通讯录”:用户输入一个域名,DNS负责查询这个域名对应的网络地址。) 更抓马的是,它费了这么大劲最后还是没找到人,反倒先把OpenAI沙箱里的漏洞给揪出来了… 消息传回OpenAI,警报随即拉响。 约两个半小时后,这次训练被人工叫停。 OpenAI随后宣布,这次事件暴露了他们在网络限制管理方面的漏洞,因此, 他们将暂停最强模型中所有涉及工具调用的训练、评测和推理任务。 @OpenAI,ber,你们最近有点忙啊。(吃瓜) AI拿DNS当电话线,训练被按下暂停键 事情发生在9月20日。 当时,模型接到的任务本身风险并不高: 依据公开博客文本和人物履历线索,找出文章作者。 测试规则也明确写了, “不许测试网络” “不许突破沙箱” 。 但很显然, 这个模型没咋把限制放在心上。 刚开始,模型走的还是正常路线。 它先用OpenAI提供的搜索工具寻找博客中的特殊短语,结果搜回来的不是音乐就是泛泛的人生建议。 眼见着搜索工具不给力,它又调用Python,直接向Google、Bing和DuckDuckGo发送请求。 然后不出意外全被拦了下来。 但它倒也没就此收手。 它一度怀疑这道题来自OpenAI的BrowseComp搜索基准,于是便从离线网页缓存中下载数据集和评测脚本,解码题库、搜索关键词。 结果还是没有搜到想要的结果。 到这一步,模型开始琢磨另一个问题: 或许有没有什么办法,能绕过OpenAI提供的搜索工具,直接摸到外面的互联网? 说干就干,它先尝试通过HTTPS访问一家公共聊天机器人服务,结果被网络代理果断拦截。 接着,它便把目光转向了 DNS 。 它发现,OpenAI虽然封住了沙箱正常上网的正门,却给部分系统依赖保留了查询DNS的窗口,它可以试着钻这个空子: 把问题藏进DNS请求里,再把外部聊天机器人的回答塞进查询结果送
编辑|Sia 媒体和舆论炸锅了。 OpenAI 的 Agent,又从沙箱里找到了一条通往互联网的路。 更麻烦的是,这一次发生在 OpenAI 已经大规模加固过安全措施之后。 9 月 20 日,一个正在接受强化学习训练的 OpenAI 内部研究模型,被要求完成一项普通的信息搜索任务:根据一篇博客文章和几条人物信息,找出文章作者。 它先老老实实用了 OpenAI 提供的搜索工具。没找到答案后,事情开始逐渐跑偏。 Agent 尝试直接访问 Google、Bing 和 DuckDuckGo,均告失败;随后继续寻找缓存页面和其他公共搜索服务。再往后,它开始主动测试自己到底能不能接触公网。 最终,Agent 找到了一个此前没有被彻底封死的口子: DNS resolver,也就是 DNS 解析器。 正常情况下,DNS 负责把域名翻译成 IP 地址。这个 Agent 却发现,可以借助 DNS 的解析和委托机制,把问题编码进请求里,让外部公共聊天机器人回答,再通过 DNS 把结果传回来。 为了确认这条路真的能用,它甚至先做了个小测试——问外部服务:法国的首都是哪里? 返回的答案是:Paris。 随后,它开始通过这条路径继续询问原本任务中的人物线索。OpenAI 明确表示,这项任务并没有要求模型测试网络控制,更没有授权它访问实时互联网,因此将这类绕过限制的行为视为 misalignment,也就是不符合预期的行为。 这条不起眼的 DNS 通道,最终让 OpenAI 再次踩下了暂停键。 刚加固一个月,Agent 又出去了 OpenAI 的监控系统其实很快就发现了异常。 Agent 第一次成功从外部获得响应后,大约 12 分钟,系统触发最高级别警报;3 分钟后,已经有人开始人工检查。OpenAI 概括称, 从异常行为发生到监控发现大约用了 15 分钟 。 但训练并没有马上停下来。 按照 OpenAI 在 Hugging Face 事件后建立的机制,发现这种异常行为后,系统原本应该自动终止训练任务。然而这套机制没有正常执行,团队内部一度对到底有没有停掉,产生了混乱。 直到 两个半小时以后 ,这轮训练才被人工关闭。 事后检查还发现,此前已经出现过其他通过 DNS 接触外部服务的尝试,其中一些没有被监控系统以应有的严重等级标记出来。OpenAI 还发现,负责侦测异常 DNS 活动的一套基础设施监
Related stories
Altman Outlines Three AI Endgames to OpenAI Staff
According to The Information, OpenAI CEO Sam Altman last week told employees about three proposals for safely developing AI: an IAEA-style international regulator, a CERN-like merger of labs, or one lab using recursive self-improvement (RSI) to 'melt everyone else's GPUs.' The report highlights the industry's ongoing debate over AI governance and the potential for extreme competitive dynamics.
1 reports · 1 sources
OpenAI retreats from strict China chip export controls, aligning with Trump
According to Politico, citing sources, OpenAI has retreated from advocating for strict US chip export controls to China ahead of the lame-duck session, aligning closer with President Trump. The report notes that Nvidia is a big winner from this shift, as OpenAI had pushed for strict limits for much of the previous year.
Anthropic's leaked AI bill draft draws criticism; Amodei defends safety approach
A leaked draft of an AI safety bill from Anthropic has drawn criticism from safety advocates for being weaker than the bipartisan FRONTIER Act, with provisions requiring judicial approval before federal agencies could block a model's release, potentially only if 50 or more people could be killed. In response, Anthropic CEO Dario Amodei defended the company's 'race to the top' approach, citing nine safety decisions with 'substantial costs,' and admitted mishandling the draft bill.
US DHS orders federal civilian agencies to remove DeepSeek AI tech
The US Department of Homeland Security has ordered all federal civilian agencies to remove DeepSeek artificial-intelligence technology from their IT systems and prohibits future procurement of its products and services, citing national security concerns. The order also covers third-party services built using DeepSeek's technology.
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe