VulnCheck questions Anthropic's Project Glasswing: 37,966 candidate vulnerabilities, only 217 fixed
Security firm VulnCheck reported that in the seven months since Anthropic launched Project Glasswing, Claude has identified 37,966 candidate vulnerabilities, but only 217 have been publicly fixed as of early November. The report notes a widening gap: nearly 12,000 new candidates emerged in the last two months, with only 15 additional fixes, and 419 retractions and 1,654 duplicates were logged, raising questions about the program's effectiveness.
Coverage timeline
量子位量子位
Anthropic玻璃翼计划被质疑!近4万个候补漏洞,只修了217条 程浅 2026-11-12 15:55:11 来源: 量子位 只管挖不管埋。 程浅 发自 凹非寺 量子位 | 公众号 QbitAI 最近AI找Bug这事儿有点太割裂了。 这一边,AI一朝出手倒查所有,先挖出了个 PHP底层重大安全漏洞 ,又扒出 948个Linux内核漏洞 …… 另一边,开源社区都快被整崩溃了:你把漏洞找出来了,你倒是修啊! 昨天,网络安全公司VulnCheck发布了一份关于Anthropic 玻璃翼计划(Project Glasswing) 的成绩单。 上面显示,在玻璃翼计划推出七个月后,Claude已累计挖出了 37966条候选漏洞 。 但截至目前,公开记录上只有217条被修复。 VulnCheck不禁质疑,当初那个轰轰烈烈的网络安全“Mythos时代”,真的到来了吗? 3.8万个漏洞,究竟修好了多少? 先帮大家回忆一下Anthropic今年4月高调宣传推出的“玻璃翼计划”。 该计划旨在利用Claude大规模挖掘关键软件及开源项目中的安全漏洞,联合科技企业、开源维护者推动漏洞修复,抢在被利用之前消除安全隐患。 取名寓意有二。 一方面,安全漏洞就像玻璃翼蝶一样,藏在人眼皮底下,数十年无人发现;另一方面,透明本身也是一种保护,Anthropic希望通过更透明的安全研究和漏洞披露机制,让软件系统获得更好的防护。 △玻璃翼蝶,学名宽纹黑脉绡蝶|图源wikipedia 启动之初,Anthropic宣称要提供1亿美元的模型使用额度和400万美元的开源安全捐款,同时还宣布它们的网络安全王炸模型 Claude Mythos Preview 已发现了数千个高危和严重漏洞。随后一呼百应,苹果、谷歌、微软、AWS、英伟达纷纷加入。 但果真如此吗? 根据VulnCheck持续追踪的数据,截至11月初,Anthropic的候选发现已达37966条,但漏洞披露台账中 标记为已修复的仅有217条 。 与此同时,作废数据还在堆积,漏洞撤回项419条,重复项高达1654条。 △图源VulnCheck 这种差距还在加速扩大。 仅在最近两个月内,候选漏洞就暴增了近1.2万条,但已修复记录却仅 微弱新增了15条 。 此外,VulnCheck追踪到的442个归因于Anthropic的CVE,仅占2026年全球公开CVE
Related stories
Anthropic: Claude flags 493 security issues across 25 open-source projects
Anthropic reported that Claude identified 493 security issues across 25 open-source projects, covering over 5 million lines of C, C++, Java, PHP, and Python code, including one vulnerability that went unnoticed for 21 years. The lab also announced a partnership with Theorem to use Claude for formally proving security properties at the assembly level across more than 100 real-world open-source libraries, extending formal verification to larger codebases.
4 reports · 3 sources460 points · 310 comments
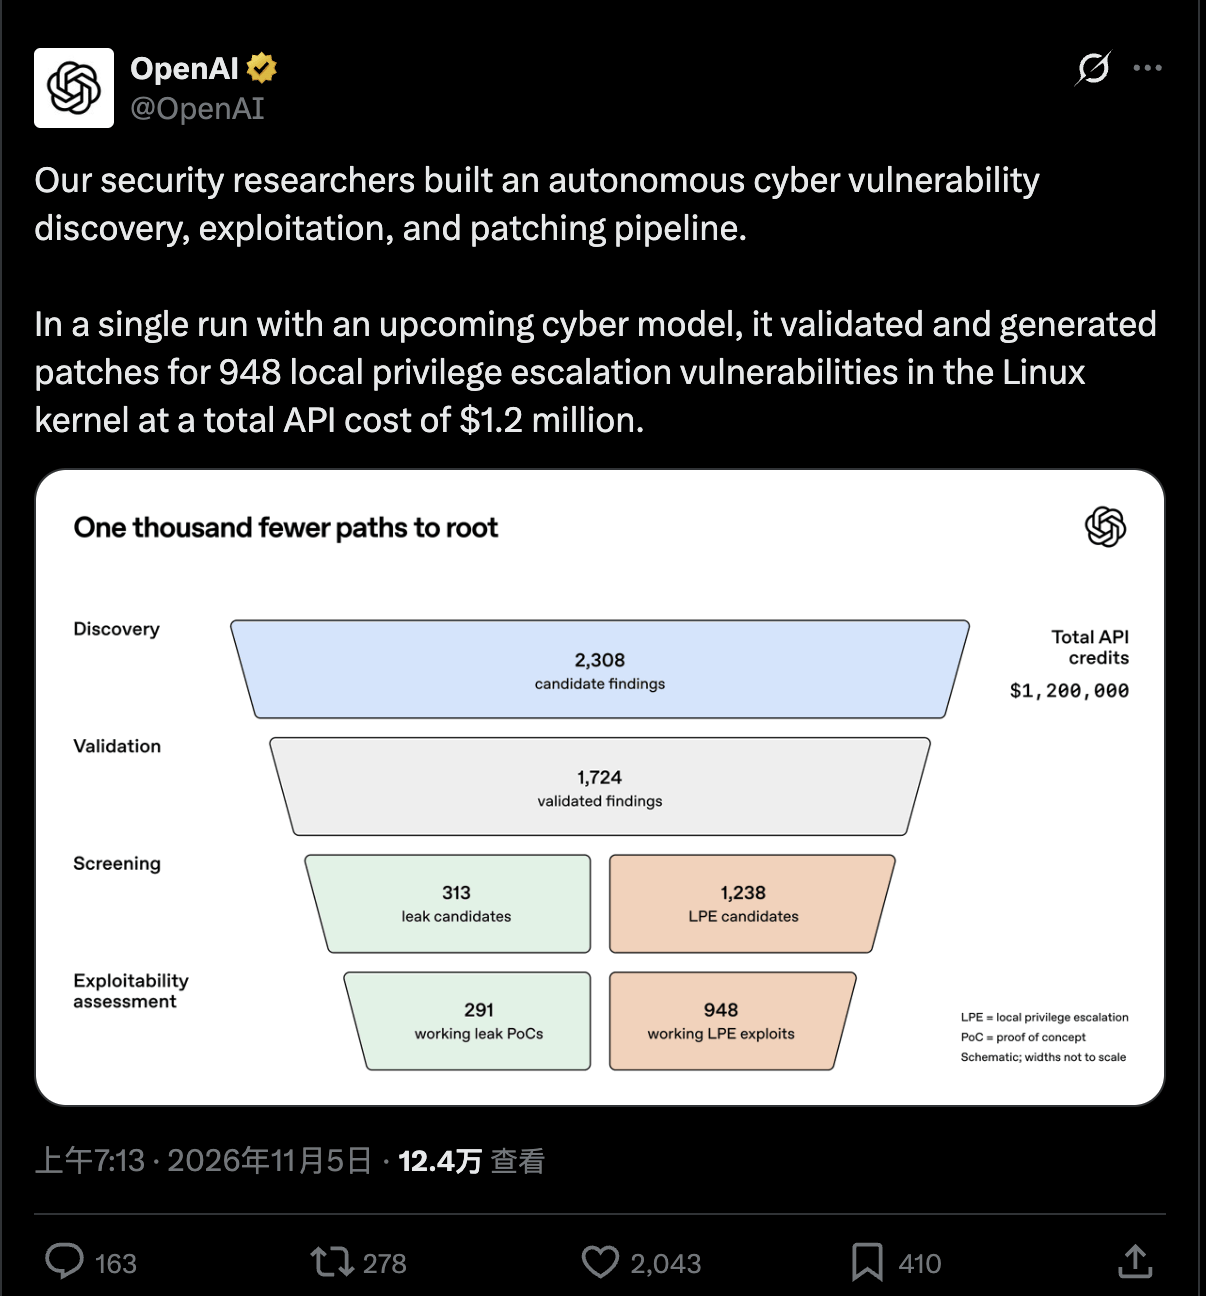
OpenAI pipeline finds, patches 948 Linux kernel privilege-escalation flaws for $1.2M
OpenAI detailed an autonomous pipeline that used an upcoming cybersecurity model to discover, validate, and generate patches for 948 local privilege-escalation vulnerabilities in the Linux kernel, at a total API cost of $1.2 million. The pipeline employed scout agents to narrow the codebase to 2.8 million high-value lines and analyst agents that produced 2,308 suspected vulnerabilities in 12 hours, with validation and exploit-writing stages following.
Anthropic files S-1 for Nasdaq IPO under ticker ANT
Anthropic, PBC filed a Form S-1 with the SEC for an initial public offering on the Nasdaq under the symbol ANT, with the number of Class A shares and price range yet to be determined. The 335-page prospectus reveals strong revenue growth, mounting losses, an unusual governance structure for founder control, and over $800 billion in long-term compute commitments.
34 reports · 8 sources1703 points · 1674 comments
PHP2Shell critical RCE flaws patched; exploited before disclosure
PHP released security updates (8.5.12, 8.4.27, 8.3.36, 8.2.35) fixing two critical unauthenticated remote code execution vulnerabilities, collectively dubbed PHP2Shell, affecting up to 70% of websites. The flaws were discovered in August by OpenAI's GPT-5.6 Sol and independently by Google's Wiz, and AWS reported exploitation starting October 17, four days before public disclosure.
6 reports · 2 sources
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe