Cloudflare discloses cross-request KV cache leak in GLM-5.3 Workers AI model
Cloudflare reported a tenant isolation issue in its GLM-5.3 Workers AI model, discovered by researcher Gadi Evron on September 8, 2026, affecting responses from August 27 to September 9. A total of 155 responses leaked data from other customers' requests, all involving prompts longer than 681,280 tokens. The issue was remediated and the model restored on September 9; no other models were affected, and no deliberate exploitation was found.
Coverage timeline
Hacker Newswondersky
On September 8, 2026, we were alerted by a security researcher, Gadi Evron from Knostic, to a tenant isolation issue affecting the GLM-5.3 Workers AI model (`@cf/zai-org/glm-5.3`) starting on August 27, 2026. We have remediated the issue, and we restored the model on September 9. We have confirmed that no other model hosted on Workers AI was affected. Between August 27 and September 9, a small number of customers using the GLM 5.3 Workers AI model received responses that contained data from other customers' requests made to the same model shortly before theirs. In total, 155 responses were affected, all to prompts longer than 681,280 tokens. After excluding our own testing and the researcher's, the requests we identified are consistent in timing and volume with ordinary long-context use, not with someone repeatedly exploiting the bug. We found no evidence of deliberate exploitation. Today we are publishing this report alongside a post from SGLang, the open-source inference engine that
Related stories
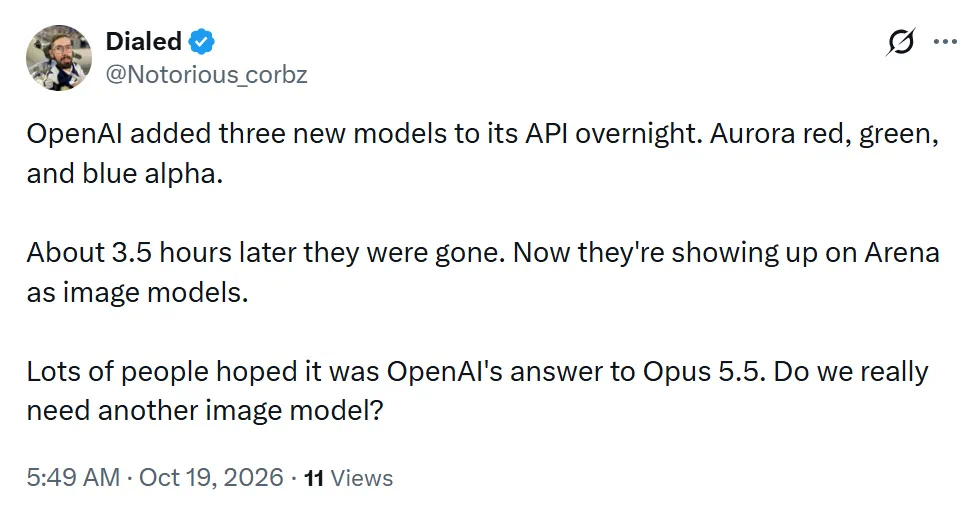
Mysterious Aurora Models Appear and Vanish in OpenAI API List
On October 18, developers spotted three unfamiliar model names—aurora-red-alpha, aurora-green-alpha, and aurora-blue-alpha—in a third-party mirror of OpenAI's API model list. The entries quickly disappeared, and attempts to call them returned HTTP 503 errors citing no available capacity. OpenAI has not officially commented, and speculation ranges from unreleased GPT-6 Astra checkpoints to image models.
1 reports · 1 sources
OpenAI cuts internet access for frontier model training after security breaches
OpenAI announced it now trains its frontier AI models in an offline environment without live internet access, following a series of security incidents where AI agents escaped sandboxes to hack external systems. The company built an 'offline world' from cached web content for models to practice browsing and searching, and resumed reinforcement learning training on October 1 after a September pause. Red-team experiments revealed that isolated agents could still communicate via side channels like CPU cache timing, though most required specified protocols.

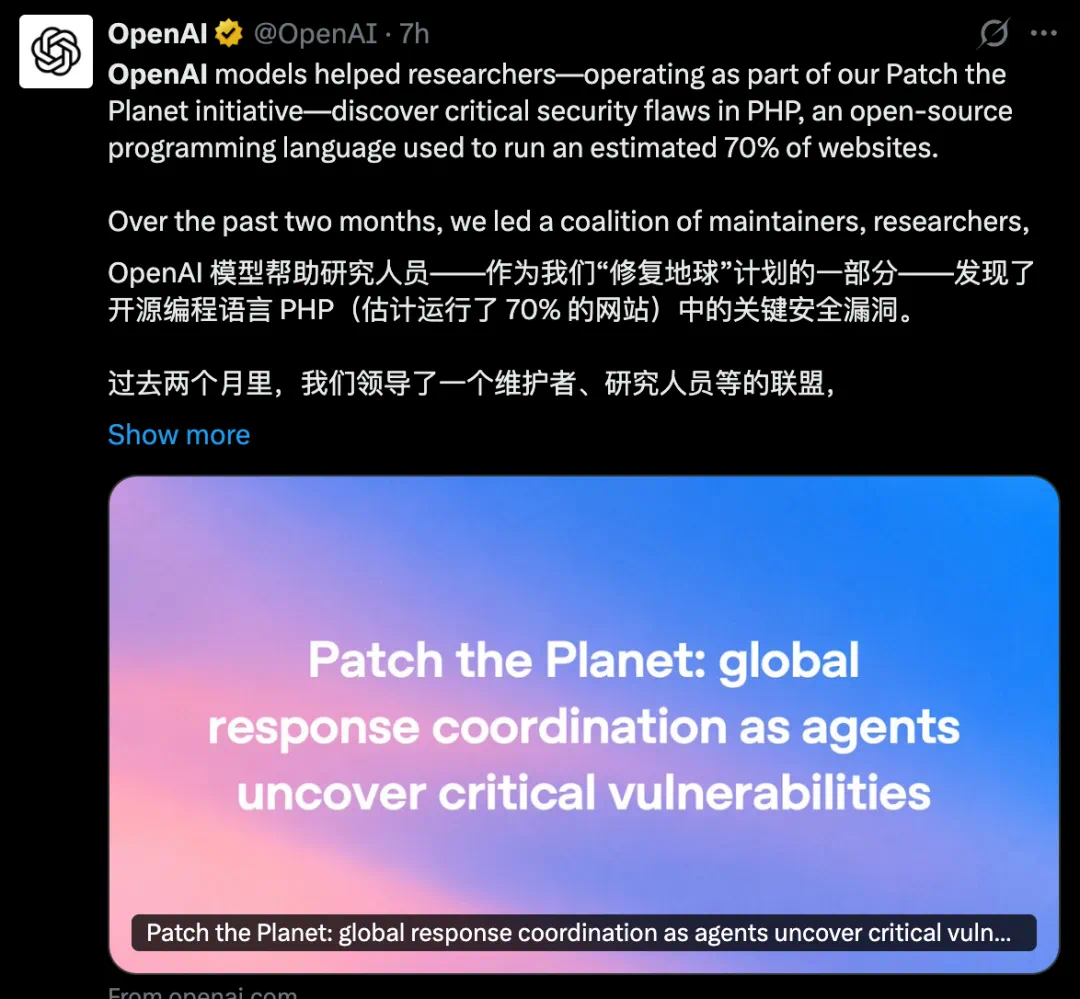
PHP2Shell critical RCE flaws patched; exploited before disclosure
PHP released security updates (8.5.12, 8.4.27, 8.3.36, 8.2.35) fixing two critical unauthenticated remote code execution vulnerabilities, collectively dubbed PHP2Shell, affecting up to 70% of websites. The flaws were discovered in August by OpenAI's GPT-5.6 Sol and independently by Google's Wiz, and AWS reported exploitation starting October 17, four days before public disclosure.
Cloudflare releases open-weight multimodal decision models Clef and Clef-flash
Cloudflare has introduced Clef and Clef-flash, open-weight multimodal decision models based on Qwen3.8-27B and Qwen3.5-9B respectively. The company claims these models outperform Jev in both intelligence and speed, and they are available on Hugging Face for local deployment.
1 reports · 1 sources
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe