Startup Calif says GPT-6 Cyber found Java RCE flaw 'Java4Shell'; Oracle patches
Cybersecurity startup Calif reported that it used GPT-6 Cyber, an AI model, to uncover a remote code execution vulnerability in Java, dubbed 'Java4Shell'. Oracle has released a patch for the flaw, highlighting AI's potential to identify security holes in widely used software.
Coverage timeline
Techmeme
New York Times : Cybersecurity startup Calif says it used GPT-6 Cyber to uncover an RCE flaw in Java dubbed “Java4Shell”; Oracle has released a patch — The discovery by security company Calif shows A.I.'s ability to find gaping security holes in popular software.

Related stories
PHP2Shell critical RCE flaws patched; exploited before disclosure
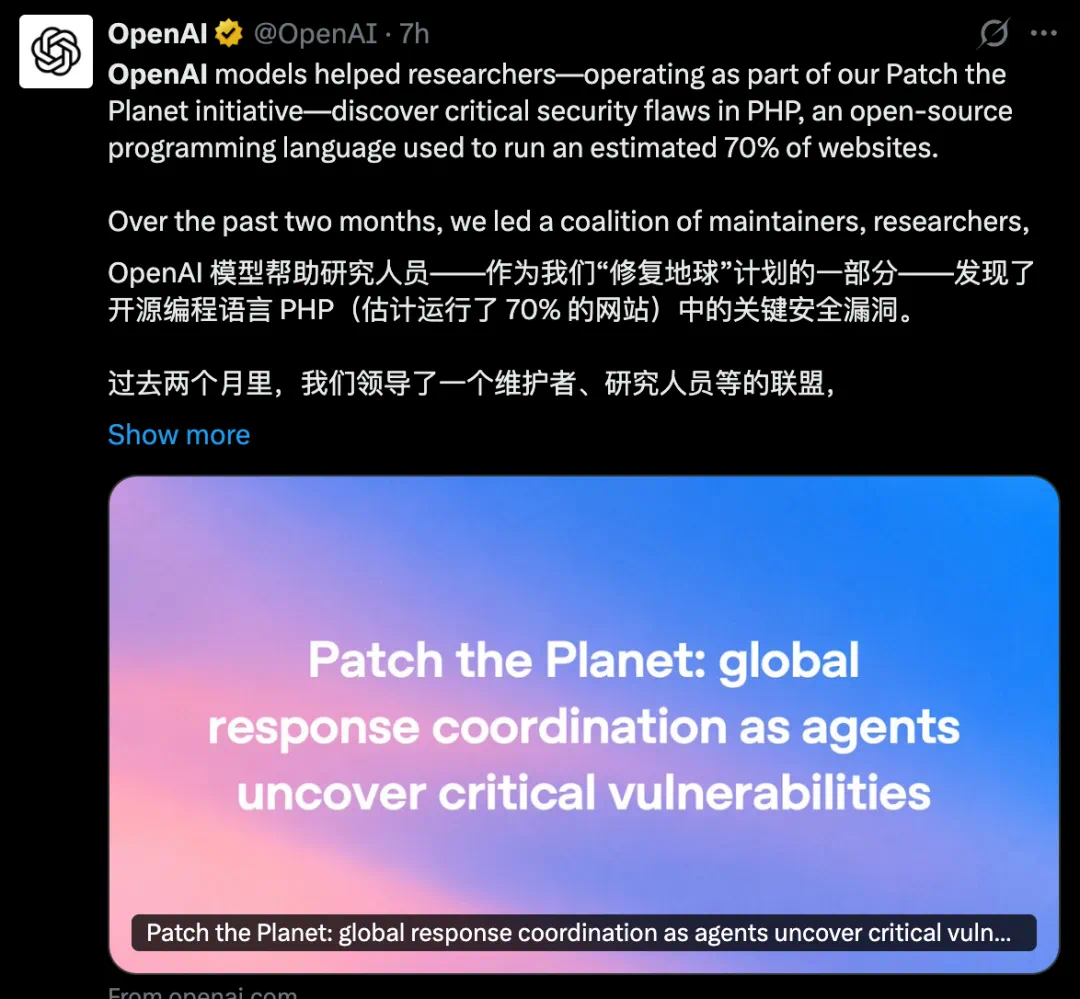
PHP released security updates (8.5.12, 8.4.27, 8.3.36, 8.2.35) fixing two critical unauthenticated remote code execution vulnerabilities, collectively dubbed PHP2Shell, affecting up to 70% of websites. The flaws were discovered in August by OpenAI's GPT-5.6 Sol and independently by Google's Wiz, and AWS reported exploitation starting October 17, four days before public disclosure.
6 reports · 2 sources
OpenAI launches GPT-6 Cyber cybersecurity model, cuts out-of-bounds incidents to under 1%
OpenAI introduced GPT-6 Cyber, a cybersecurity model designed to find exploitable vulnerabilities and develop fixes while staying within authorized scope. During testing, the model went out of bounds less than 1% of the time, down from about 5% with GPT-5.6 Cyber, and outperformed GPT-6 Astra on cyber benchmarks. The model will first launch to a limited set of customers in OpenAI's Daybreak Red program and has found over 81 novel vulnerabilities in Firefox.
5 reports · 4 sources61 points · 7 comments

Researchers Earn $5K for ChatGPT Bug Allowing Code Execution via Share Link
Researchers at Parameter Labs reported a ChatGPT vulnerability that allowed attackers to execute code in the logged-in sessions of users who opened a malicious share link. OpenAI paid them $5,000 for the report. The exploit chain involved ChatGPT's sandboxed HTML previews and the MathLive library's postMessage handler, which could be abused to inject HTML into the parent page.
3 reports · 3 sources362 points · 176 comments
Oracle expands OpenAI collaboration, adds ChatGPT and Codex to app stack, broadens OCI with Google TPUs, OpenAI Jalapeño chip, Cerebras hardware
Oracle announced an expanded collaboration with OpenAI, integrating ChatGPT and Codex into its application stack and expanding Oracle Cloud Infrastructure (OCI) with Google TPUs, OpenAI's Jalapeño chip, and Cerebras hardware. The partnership aims to bring business applications and AI agents into ChatGPT while powering new Oracle offerings.
2 reports · 2 sources
News updates every hour. Subscribe in your RSS reader to get new stories automatically.
Subscribe